Some frameworks require you to report actively exploited vulnerabilities and severe incidents to authorities within fixed deadlines, often in several stages. Nuxy works out the deadlines, prepares the content of each stage and keeps a record of what you submitted. You submit the report yourself on the receiver's own platform: Nuxy does not send anything automatically.
Start a Report
A report starts from what you learned:
- A vulnerability: on the vulnerability record, choose Confirm Actively Exploited. See Triage Vulnerabilities.
- An incident: on the incident case, choose Needs Reporting. See Handle Vulnerability Reports and Cases.
Enter the Time of Awareness: when you became aware. The deadlines count from this moment, so record it accurately. If you enter a later time than Nuxy expects, give the reason. Then choose which reports to create; Nuxy lists the reporting requirements that match the product and its markets.
Follow the Deadlines
Open Security Center → Reporting. Each report shows its Current Stage and the time left until its deadline. Overdue stages are marked Overdue. The Dashboard also lists stages that are due soon.
Fill In and Submit Each Stage
- Open the report and select the stage to work on.
- Fill in each field. Every field explains what it needs and gives an example. Fields that repeat information from earlier stages or from the vulnerability record are filled in for you.
- When the stage is complete, open the receiver's web form and copy each value across with Copy. The counter shows how many values you have copied.
- After submitting on the receiver's platform, choose Record Submission and enter the submission time and the reference the receiver gave you.
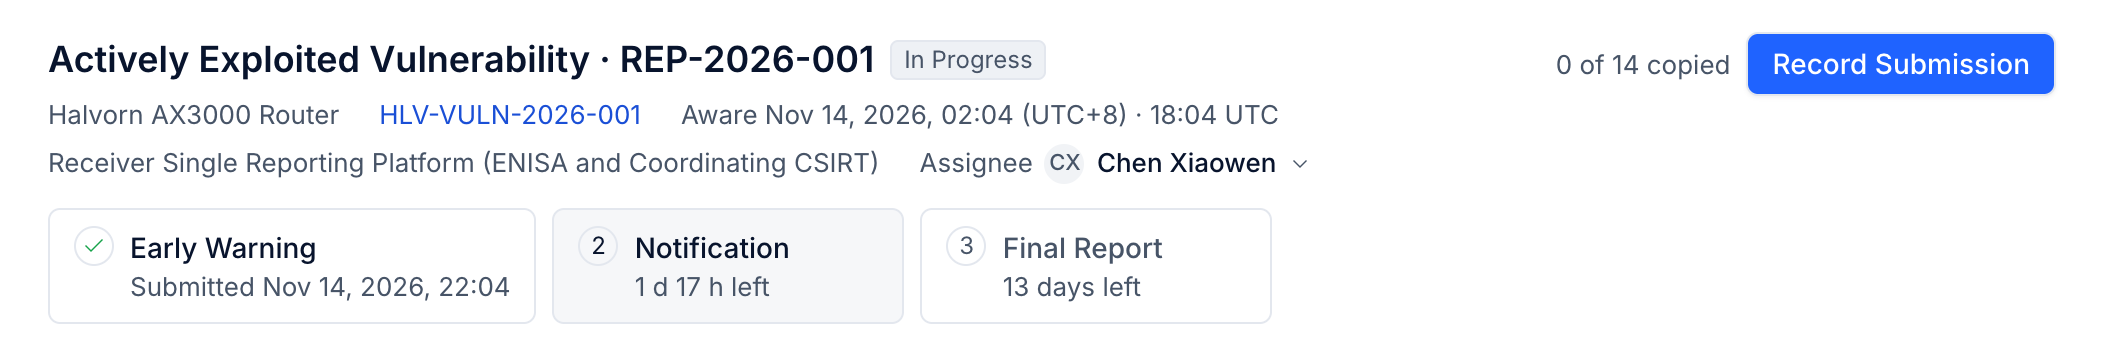
A stage can only be recorded once the stage before it has been. Some stages are only needed when the receiver asks for them; choose Receiver Asked for It when that happens.
Inform Affected Users
Many reporting rules also require you to tell the affected users. When you publish a security advisory for the vulnerability, choose it on the report to record that users were informed; or record that you informed them by other means, how and when.
Corrective Measures
The report also tracks when a fix or mitigation became available, taken from the vulnerability record's fixed version or an interim advisory. Use Change if it should come from somewhere else.